Mailheight

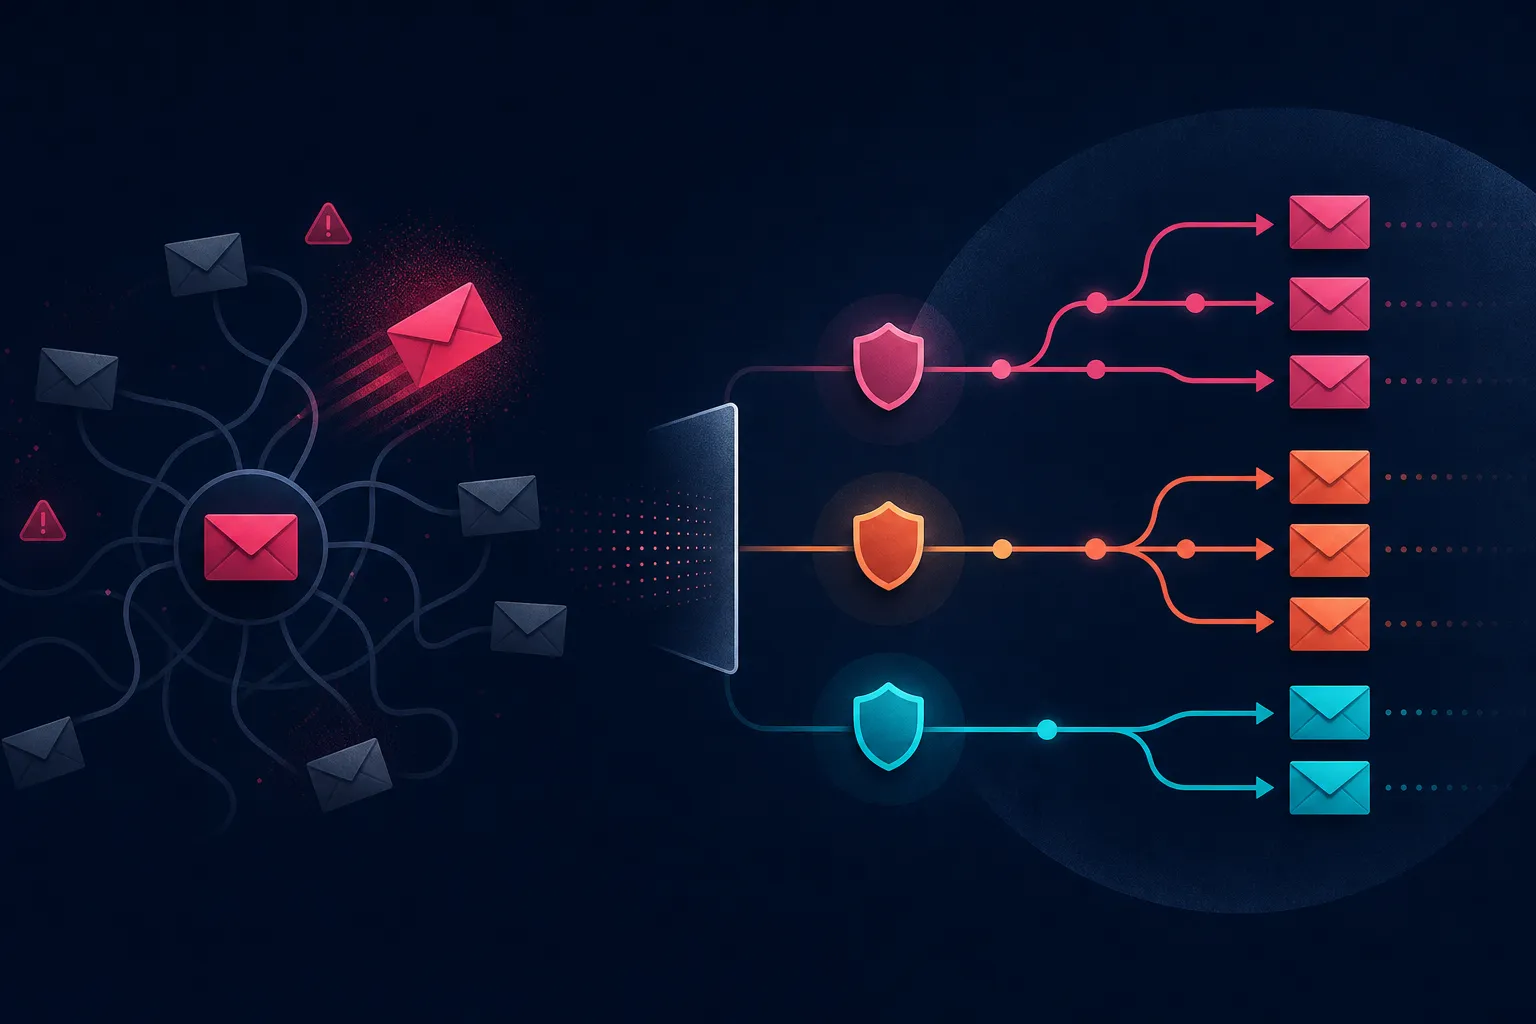
The shared account problem
Picture a team that keeps its entire budget in one shared account. One employee moves a small amount without approval. The account freezes. Nobody can touch the funds. The project stalls. The team scrambles. One person's action hits everyone.
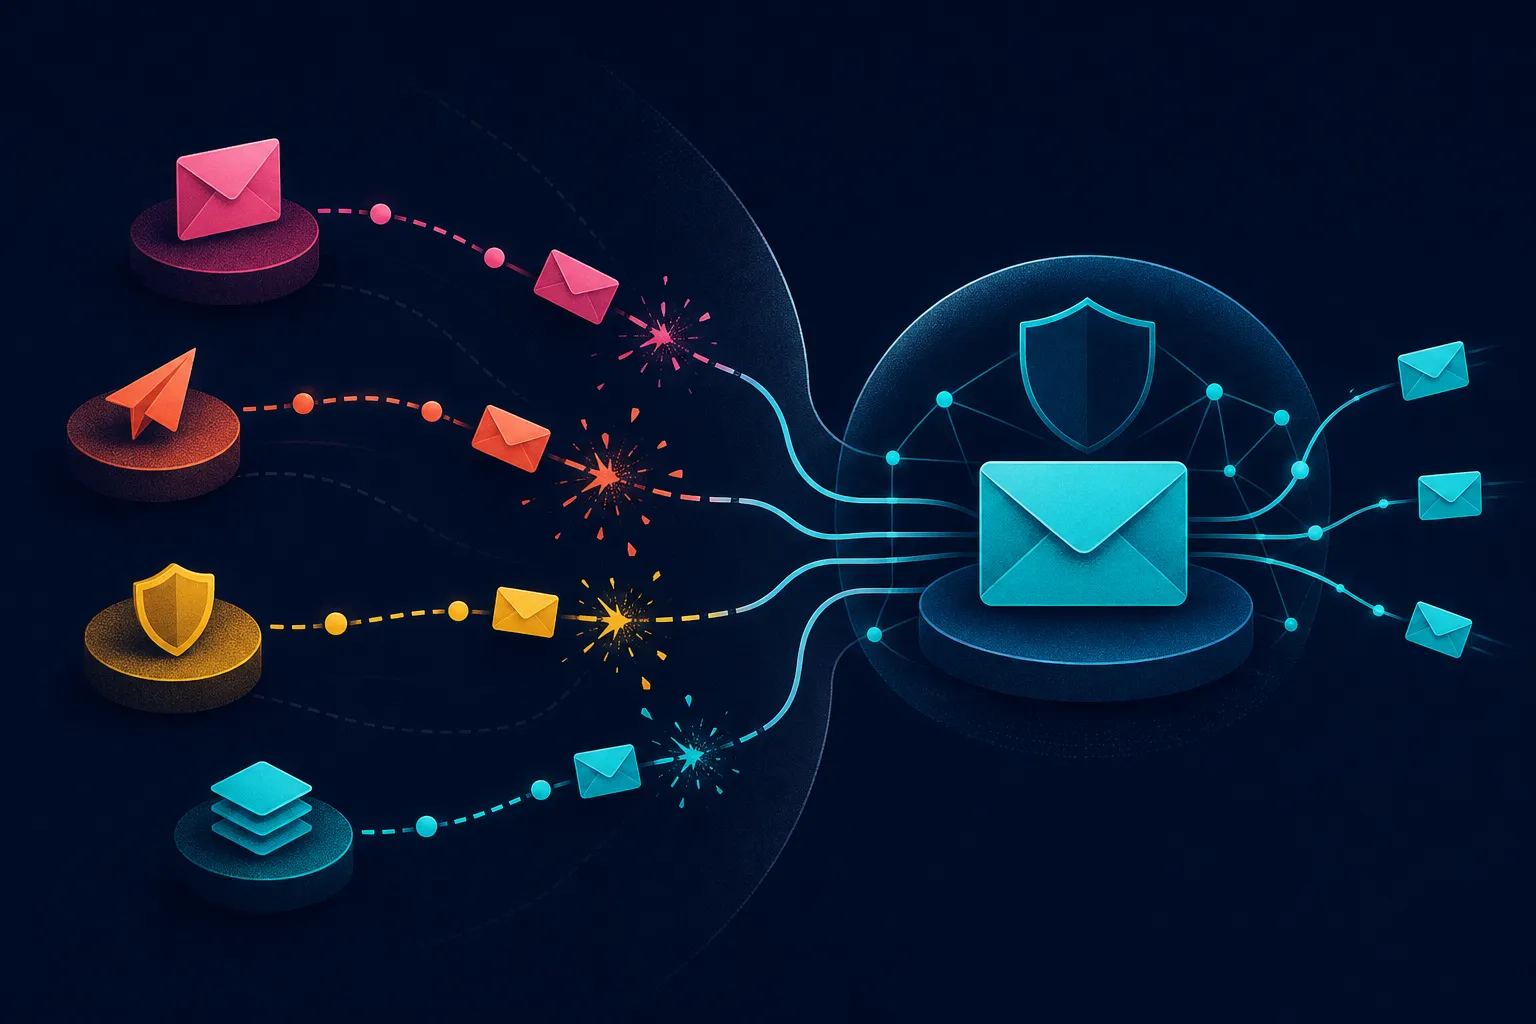
Agency sending runs on the same logic. You may have ten clients under one roof. Nine keep clean data, controlled volume and sensible campaigns. Then one client uploads a poor list, pushes too much volume or starts generating complaints. If the underlying operation is shared, that client's problem can become everybody's problem.
This idea was laid out well in the original LinkedIn post by Nithyanandan Ramakrishna, and it is worth expanding for any agency running outbound email at scale. The core point: shared trust is only as strong as the least careful hand.
Why shared sending infrastructure is risky
Email reputation is not a single number that lives in one place. It is built from many signals tied to your sending domain, your IPs, your authentication setup and the behavior of the mail you send. When several clients send through the same underlying setup, those signals blend together.
That blending creates a few predictable risks:
- Volume contamination. One client ramps up sends too quickly and the shared infrastructure absorbs the spike. Providers see a sudden change in behavior from the same source.
- List quality contamination. A client uploads a purchased or poorly cleaned list. Bounces and complaints rise, and the reputation hit lands on infrastructure everyone else depends on.
- Complaint spillover. Recipients who mark one client's mail as spam are signaling about the shared sending source, not just that one campaign.
- Capacity contention. One client's heavy sending day can consume the throughput the other nine need to hit their own schedules.
None of these require bad intent. They happen because convenience and shared setup make it easy for one weak link to reach everyone.
What separation actually looks like
The safeguard is separation, and you can build it in. The post describes how MailHeight separates client operations with client-specific senders, sending limits, lists, rules and reporting. That list is a useful checklist for evaluating any platform you use for agency outbound.
Client-specific senders
Each client should send from its own verified domain and sender identity. This keeps authentication records, domain reputation and bounce handling tied to that client rather than pooled across the agency. If one client's domain runs into trouble, the others are not dragged down with it.
Client-specific sending limits
Daily and hourly limits should be set per client, not shared across the whole account. This prevents one client from consuming another client's sending capacity and keeps each client's volume pattern predictable to mailbox providers.
Client-specific lists and rules
Suppression lists, exclusion rules and audience definitions should live at the client level. A suppression that applies to one client should not silently apply to another, and a list problem for one client should not become an agency-wide incident.
Client-specific reporting
When reporting is pooled, you cannot tell which client is driving a bounce spike or a complaint increase. Per-client reporting lets you spot a problem early and fix it before it spreads.
The sending layer still needs its own guardrails
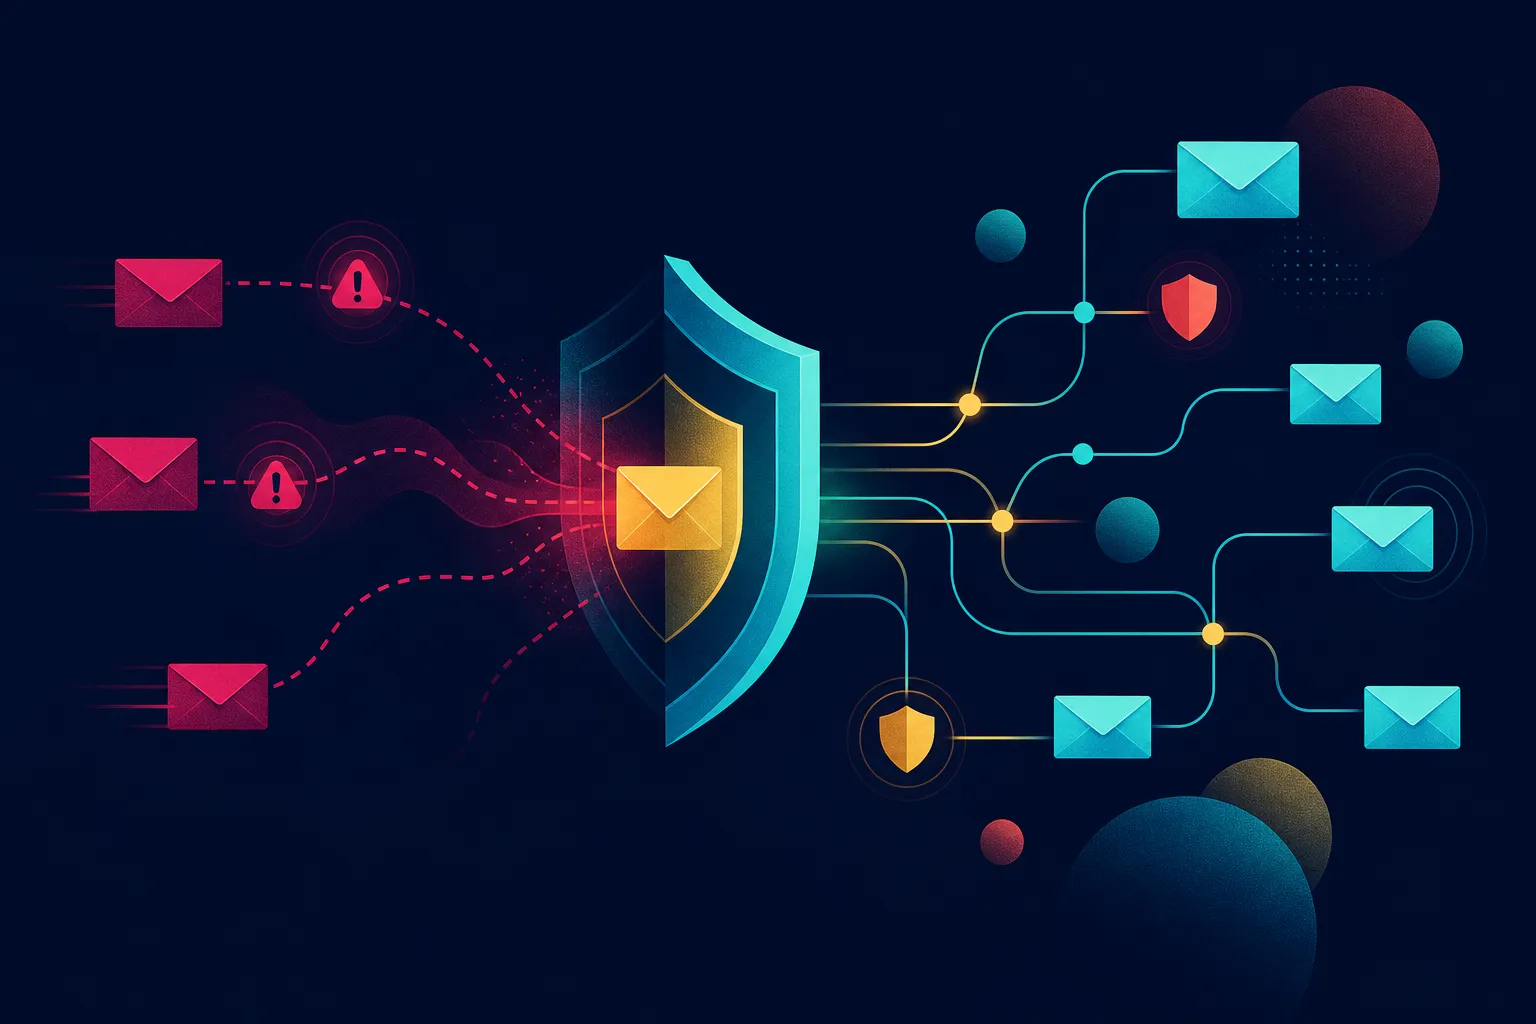
Separation between clients is necessary, but it is not the whole picture. The post also notes that the sending layer applies company-level spacing, mailbox-provider pacing, daily and hourly limits, authentication checks and sender-health monitoring.
These are the controls that keep any single send within safe bounds:
- Spacing and pacing spread messages out so you are not hitting a mailbox provider with a burst it reads as suspicious.
- Authentication checks confirm that SPF, DKIM and DMARC are set up correctly before mail goes out. Misconfigured authentication is one of the most common and most avoidable causes of deliverability trouble.
- Sender-health monitoring watches the signals that matter, such as bounce rates and complaint rates, so you can act before a small issue becomes a blocklisting event.
Put simply: separation keeps clients from affecting each other, and the sending layer keeps each client's mail within healthy limits. You need both.
A practical way to audit your current setup
If you are not sure how much your clients currently share, ask these questions about your platform:
- Do clients send from separate domains and sender identities, or is everything routed through one shared setup?
- Are daily and hourly limits configured per client, or is there one pool for the whole account?
- Are suppression lists and audience rules scoped to each client?
- Can you see bounce and complaint data broken out by client?
- Does the platform check authentication before sending and monitor sender health over time?
Any "no" is a place where one client's mistake can reach the others.
Separation is part of the architecture, not an add-on
The post closes on a line worth repeating: shared infrastructure is convenient until the least careful hand touches it. Convenience is real, and agencies are busy. But the cost of a shared incident, in lost sending capacity, damaged reputation and client trust, usually outweighs the setup effort.
You have several reputations operating under one roof. One client should not consume another client's sending capacity. One client's list problem should not become an agency-wide incident. One client's campaign should not determine how the other nine are allowed to send.
Treat separation as part of your sending architecture from the start. Set up client-specific senders, limits, lists, rules and reporting, then layer company-level pacing, authentication checks and sender-health monitoring on top. That combination is what lets an agency grow its client roster without growing its risk at the same rate.