Mailheight

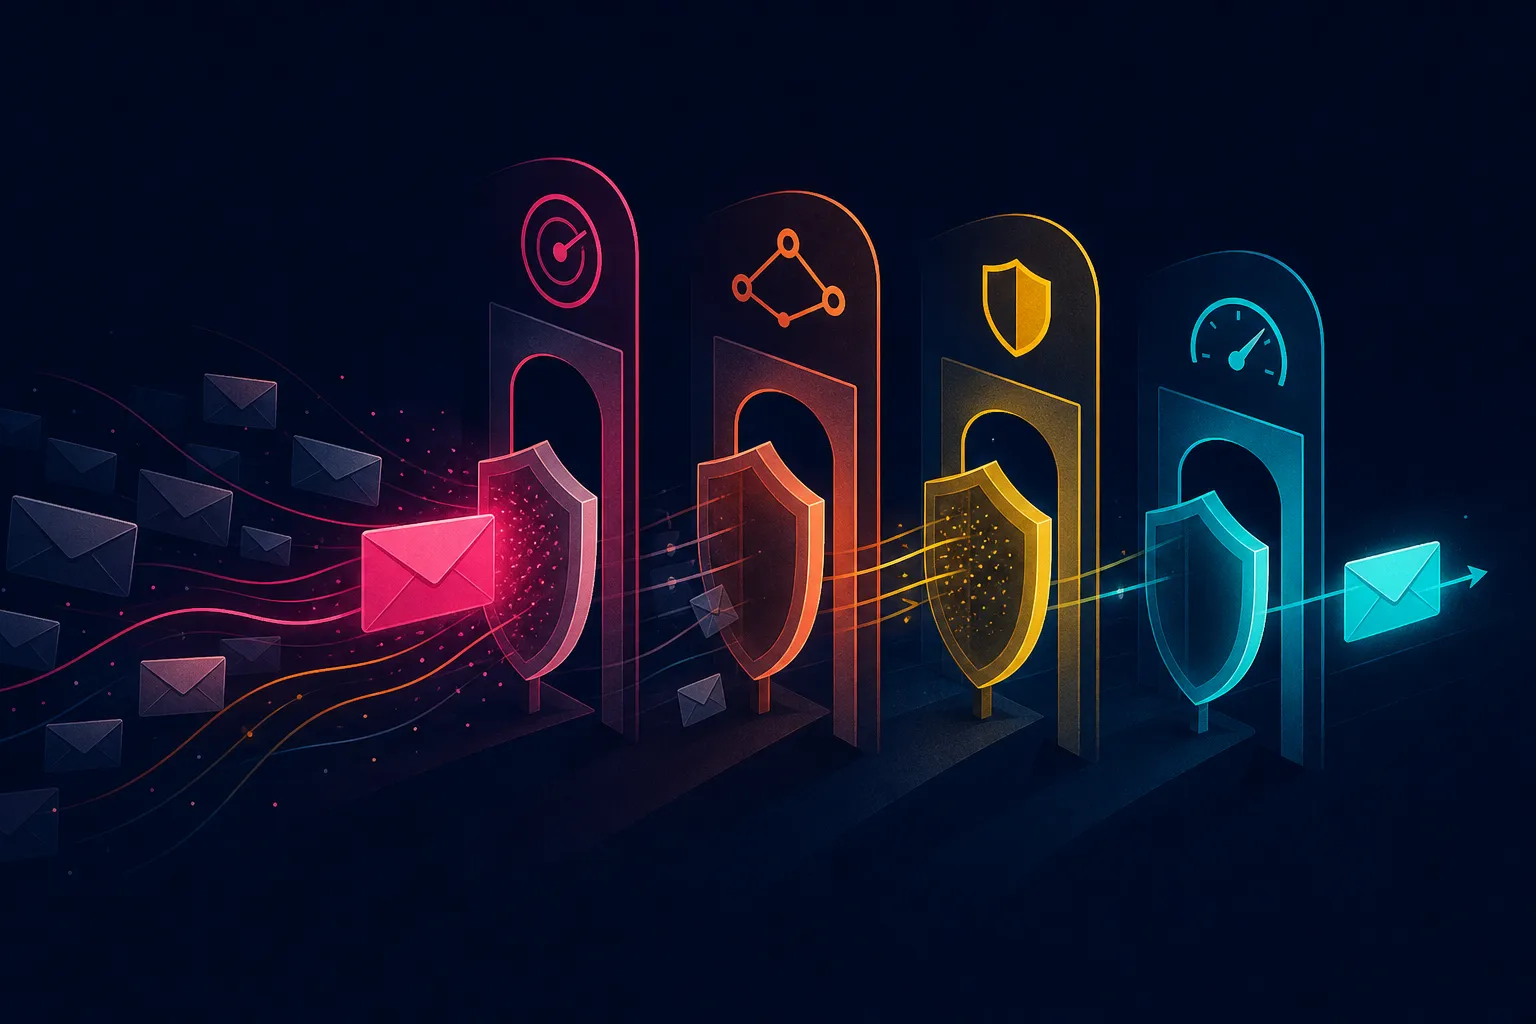
Most cold email advice focuses on the things you can see: subject lines, personalization, offer copy, follow-up sequences. But on a receiving server, none of that gets evaluated first. The order of operations is fixed, and it starts with the identity that opened the socket.
As Nithyanandan Ramakrishna put it in the original LinkedIn post, your IP is judged before your subject line is read. That is the order of operations on a receiving server, and it is not negotiable.
The Block Happens Before the Message Exists
When your sending server connects to a receiving server, the first thing that happens is the connection banner exchange. This is the SMTP handshake, and it occurs before EHLO, before MAIL FROM, before the message headers, and long before anyone reads a word of your copy.
According to the post, Proofpoint returns a 554 at the connection banner, before EHLO. Nothing about the message has been read yet. No subject line, no personalisation, no offer. The decision was made on the identity that opened the socket.
Microsoft 365 behaves the same way at the source IP level, returning 550 5.7.606-649, Access denied, banned sending IP, before message content is considered.
The practical implication is uncomfortable but simple: copy, subject lines and personalisation sit downstream of a decision that has already happened. A blocked IP never gets to show its copy. You can spend a week A/B testing subject lines and still see nothing but silence, because the rejection happened at a layer your copy never reaches.
Stop Treating Deliverability as One Thing
The post makes a useful structural point: it helps to stop treating deliverability as one thing. There are four gates: IP, identity, domain, recipients. Each is judged separately, and each can fail on its own.
This framing matters because agencies often diagnose the wrong gate. Consider these common mismatches:
- A clean domain does not save a blocked IP. If your sending IP is on a blocklist or has a poor reputation, the domain's authentication records are irrelevant at that moment.
- A good list does not save a domain with a broken authentication record. If SPF, DKIM, or DMARC are misconfigured, even a perfectly curated list of engaged recipients will see filtering and rejection.
- A strong offer does not save a recipient gate failure. If you are hitting spam traps, role accounts, or addresses that generate complaints, the content never mattered.
Each gate is evaluated on its own terms. Fixing one does not compensate for another.
The Direction of the Check Matters
One of the most useful reframes in the post is about direction. You do not check blocklists. The receiver checks you.
This sounds obvious, but it changes what you should be monitoring. Most sender-side checklist advice is pointed the wrong way, which is why a sender can work through every item on it and still see nothing but silence. A checklist that asks "is my subject line good?" or "is my list clean?" is asking about things the receiver has not looked at yet.
The gate is checked before the message, so the thing worth watching is the sending identity itself, continuously, across every mailbox provider and domain you send from, not the draft.
What the Four Gates Actually Mean
Gate 1: IP
This is the reputation of the IP address that opens the connection. It includes blocklist status, sending history, volume patterns, and whether the IP is shared or dedicated. A shared IP means your reputation is partly determined by other senders on that IP. A dedicated IP means you own the warmup process and the consequences.
Gate 2: Identity
This covers the sending identity: the envelope sender, the From domain, and the alignment between them. Authentication results (SPF, DKIM, DMARC) are evaluated here. If your authentication is broken or misaligned, the receiver has reason to distrust the message regardless of content.
Gate 3: Domain
Domain reputation is tracked separately from IP reputation by most major providers. A domain with a history of high complaint rates or spam trap hits carries that history with it, even if you move to a new IP. Conversely, a fresh domain with no history may be treated with more caution than an established one.
Gate 4: Recipients
This is where list quality, engagement, and complaint rates live. Even if the first three gates pass, a recipient gate failure (high bounce rate, spam complaints, low engagement) will degrade your reputation over time and eventually affect the earlier gates.
Why Monitoring the Draft Is the Wrong Instinct
If the gate is checked before the message, then the highest-leverage thing you can monitor is not the draft. It is the sending identity itself, continuously, across every mailbox provider and domain you send from.
In practice, that means tracking:
- Blocklist status across major providers, checked regularly rather than once
- Authentication health for every domain you send from
- Bounce and complaint rates by domain and by IP
- Inbox placement, not just delivery rates
On that last point, it is worth distinguishing delivery from placement. Delivery means the receiving server accepted the message. Inbox placement measures whether the message reached the primary inbox instead of being filtered into spam. A high delivery rate can coexist with poor placement, which is why delivery alone is a weak signal.
A Note on Blacklist Recovery
If you do find yourself blocked, the recovery process matters as much as the diagnosis. A related post in the same thread from Chigozie Abawulem offers a sensible sequence: confirm the blacklist, find the root cause, fix the problem first, gather proof of what you fixed, submit the removal request through the provider's official process, and monitor after removal.
The key warning there is that submitting a removal request before fixing the actual problem can make things worse. Getting delisted does not automatically restore deliverability. The goal is not just to get off a blacklist, it is to avoid ending up there again.
What to Do With This
The order of operations on a receiving server is not something you can negotiate. The IP is judged first. The identity is judged next. The domain and recipients follow. Your copy is evaluated last, if it is evaluated at all.
So the practical takeaway for agencies running cold outreach is to shift attention upstream. Audit the sending identity before you audit the draft. Monitor reputation continuously rather than reactively. And when a campaign underperforms, ask which gate it is actually failing at, rather than assuming the problem is in the message.
As the original post asks: which gate is your last campaign actually failing at, and would you know from the data you have?